
Linux Privileged Access Management in 2026: 9 Tools Compared
 Peter Cummings
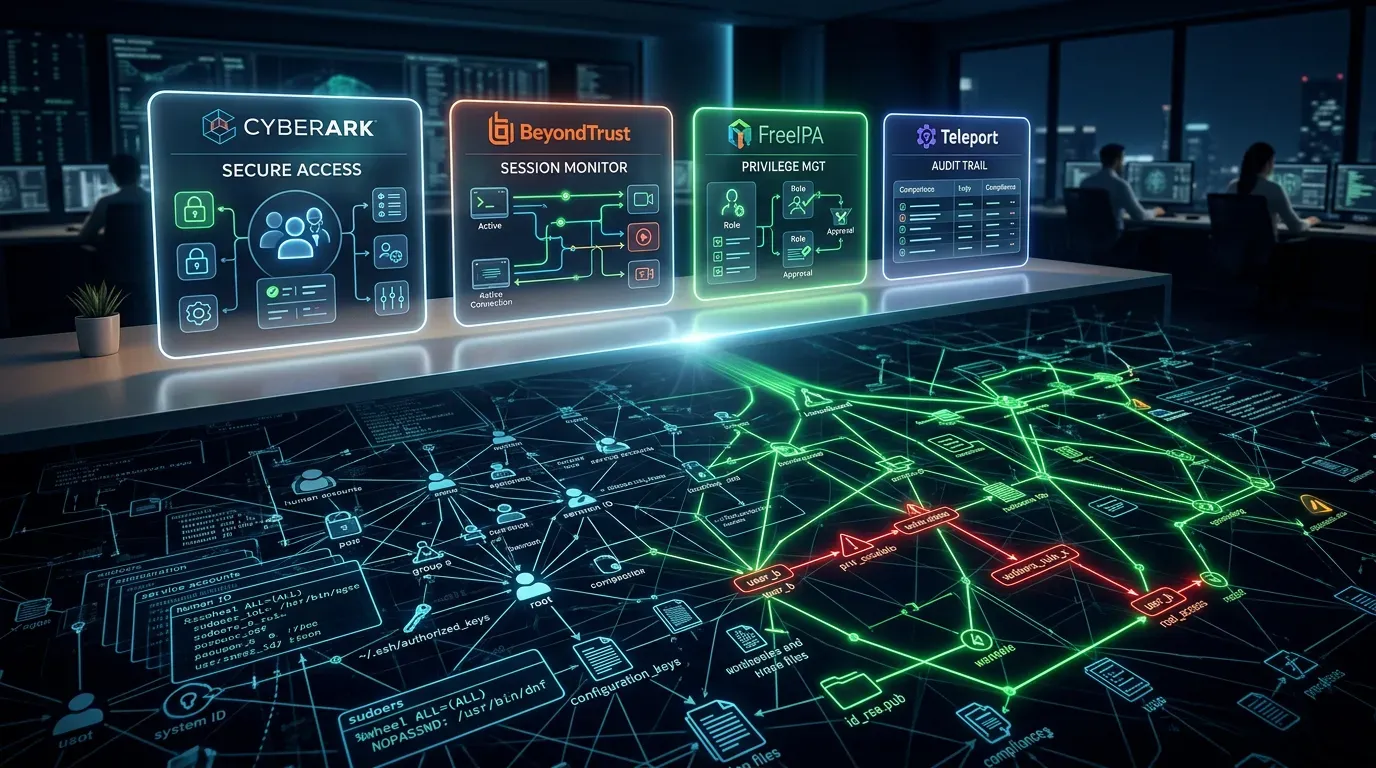
Linux privileged access management tools fall into five groups: credential vaults and session brokers (CyberArk, Delinea), privilege elevation (BeyondTrust), identity management (FreeIPA), access proxies and secrets brokers (Teleport, StrongDM, HashiCorp, Okta Privileged Access), and privilege visibility and posture (LinuxGuard). They solve different problems, and most estates need more than one.
Jump to the comparison at a glance.
The Wrong Question Is Costing You
When a security team goes looking for a "Linux PAM solution," they are usually asking the wrong question.
The right question is not which PAM tool should we deploy? The right question is: does our team actually know what every user can do on every Linux server right now?
If the answer is no — and across most enterprise environments it is — then no amount of session recording, credential vaulting, or just-in-time access provisioning will close that gap. You are securing the known door while leaving the basement unlocked.
This page compares nine tools that organisations commonly evaluate when they set out to secure Linux access: CyberArk (being rebranded Idira), BeyondTrust, FreeIPA, Teleport, Delinea, StrongDM, HashiCorp Vault and Boundary, Okta Privileged Access, and LinuxGuard. They are not competing for the same job. Understanding what each one actually does is the fastest way to stop buying the wrong solution — or to understand why the solution you already have is not enough.
Why Linux Access Management Is a Different Problem
Enterprise security stacks were built for Windows Active Directory and cloud IAM. Linux identity lives somewhere else entirely: in /etc/passwd, /etc/sudoers, PAM module stacks, authorized_keys files, and group memberships accumulated across years of role changes. Generic tools cannot see the Linux identity layer at all. In this article, PAM means privileged access management, not Linux-PAM, the Pluggable Authentication Modules framework.
The consequences are predictable. According to CrowdStrike's 2025 Global Threat Report, 79% of modern enterprise attacks use no malware — attackers simply log in using legitimate credentials or misconfigured access paths. The IBM Cost of a Data Breach Report 2025 places the mean time to identify and contain a credential-based breach at 241 days. The average cost: $4.44 million.
The common thread across those breaches is not a missing patch or a zero-day. It is a sudo rule that should have been removed six months ago, a service account with membership in a privileged group, or an SSH key that points to an account that no longer exists. None of those show up in session recordings. None of them are found by vulnerability scanners. None of them are inside a PAM vault.
That is the gap this comparison is designed to help you evaluate.
How to Evaluate Linux Privileged Access Management Tools
Before comparing tools, agree on what you are trying to measure. Most PAM evaluation checklists are built for Windows environments and miss the Linux-specific controls that determine your real exposure.
The five criteria below reflect what Linux-native identity governance actually requires.
1. Linux-Native Coverage
Does the tool truly understand Linux identity in the real world — including sudoers files, PAM module stacks, NSS configurations, setuid binaries, authorized_keys entries, and local group memberships — or is it just managing a curated set of “known” privileged accounts and leaving everything else in the dark?
2. Sudo Governance
Can the tool inventory, analyse, and risk-score every sudo rule across your fleet — including NOPASSWD entries, wildcard permissions, and GTFOBins-exploitable commands — without requiring manual server-by-server review? Sudo is the primary privilege escalation mechanism on Linux. Most tools don't touch it. For the mechanics, see our guide to sudo drift detection.
3. SSH Key Lifecycle
SSH keys are permanent until manually revoked, frequently shared across users and systems, and almost never audited. Can the tool map every authorized_keys entry across your estate, identify orphaned and shared keys, detect unauthorised additions in real time, and produce an audit trail for regulators?
4. Non-Human Identity (NHI) Support
Non-human identities — service accounts, API keys, pipeline credentials, CI/CD tokens — outnumber human identities 109:1 across the enterprise (Palo Alto Networks, 2026 Identity Security Landscape). Can the tool govern service account group memberships, detect privilege creep in automated identities, and produce compliance evidence for NHI access paths?
For non-human identity on Linux in detail, see our dedicated guide.
5. Compliance Evidence Quality
When your NIS2 auditor, DORA supervisor, or PCI QSA asks for evidence of access controls on your Linux estate, what can the tool produce? Session logs are not access control evidence. Evidence means: a structured inventory of who had what privilege, on which servers, over what time period — mapped to the specific framework control being tested.
Linux Privileged Access Management Tools Compared
CyberArk: Credential Vaulting and Session Brokering
What it is: The market leader in enterprise privileged access management. Palo Alto Networks announced the Idira brand for the CyberArk portfolio on 12 May 2026, with a phased rollout from 31 May 2026. The rename is in progress rather than complete: the first phase is branding only, the products and their architecture are unchanged, and some, the certificates and PKI portfolio among them, keep the CyberArk name for now (CyberArk’s FAQ). This article keeps the name most readers still search for. CyberArk's core capability is credential vaulting and privileged session management — it stores and rotates privileged credentials, brokers access to target systems, records privileged sessions, and increasingly operates as a unified identity security platform spanning cloud, on-prem, and OT/ICS environments.
What it does well on Linux: CyberArk has substantive Unix/Linux capabilities. Its Privileged Access Manager automatically discovers accounts and credentials across on-premises and cloud infrastructure, onboards them to a tamper-proof digital vault, and enforces automated rotation. Session isolation and recording is available for brokered Linux connections, and it supports just-in-time, zero-standing-privilege access for cloud-native workloads. CyberArk also now offers a dedicated SSH Manager for Machines product, designed specifically to secure SSH-based machine identities — a meaningful step toward the non-human identity problem. For session-level audit trails across mixed estates, CyberArk is a genuine enterprise-grade platform.
What it does not do: CyberArk manages the accounts it has onboarded. It does not map the sudoers topology across your estate, inventory local accounts outside its managed set, analyse privilege escalation paths through GTFOBins chains, or produce a comprehensive picture of who can do what across the Linux identity plane — as opposed to who did what inside a brokered session. The privilege topology that exists outside vaulted accounts — and on most estates this is the majority of the attack surface — is not CyberArk's scope. SSH Manager for Machines governs the machine identities you enrol; it does not discover and audit the SSH key sprawl that already exists across your estate.
Deployment reality: CyberArk is a large platform with significant deployment and licensing complexity. Implementations typically take months and require dedicated professional services. It is built for organisations that have the resource to operate it at scale.
Best suited for: Large enterprises with complex, multi-platform environments that need credential vaulting, session brokering, and unified privileged access governance across Windows, Linux, and cloud — and have the budget and resource to deploy and maintain the platform.
BeyondTrust: Endpoint Privilege Enforcement
What it is: BeyondTrust's Endpoint Privilege Management (EPM) for Linux replaces sudo with a centrally managed privilege elevation layer. Rather than vaulting credentials, it intercepts privilege elevation requests at the endpoint and enforces policy — allowing or denying commands based on rules, user context, and risk profile.
What it does well on Linux: BeyondTrust takes sudo governance seriously. EPM for Linux can replace sudo directly, centralise policy management across your fleet, and produce granular command-level audit logs. For organisations that need fine-grained control over what privileged commands users can run — and want that control enforced at the OS level — BeyondTrust EPM is a credible solution.
What it does not do: BeyondTrust manages the access it controls. It does not discover and inventory existing sudo configurations before you deploy, produce a historical privilege map of your estate, audit SSH key sprawl, govern service account memberships, or generate compliance evidence for the Linux identity posture that existed before the tool was installed. It is a control tool, not a visibility tool. You must already know what you have before it can protect it.
Deployment reality: EPM for Linux requires agent deployment across your fleet. Agent-based deployments carry change management overhead, particularly in regulated environments where production changes require CAB approval. Better suited for endpoints and developer workstations than for large heterogeneous server estates.
Best suited for: Organisations that need fine-grained sudo policy enforcement and command-level audit trails, particularly on endpoints and developer workstations running Linux.
FreeIPA: Centralised Linux Identity Management
What it is: FreeIPA (also available as Red Hat Identity Management / IdM) is an open-source identity management solution for Linux/Unix environments. It integrates LDAP directory services, Kerberos authentication, DNS, and host-based access control into a single platform, providing centralised identity management for Linux fleets.
What it does well on Linux: FreeIPA is genuinely Linux-native. It manages users, groups, host-based access control policies, and sudo rules centrally — and for organisations building out their Linux identity infrastructure from scratch, it provides a solid foundation. It is free (the software itself), well-documented, and integrates naturally with Red Hat/CentOS environments.
What it does not do: FreeIPA manages what is enrolled in its directory. It does not discover or govern identity on systems that predate the deployment, audit the gap between policy and reality across a heterogeneous estate, produce compliance evidence mapped to NIS2 or DORA controls, or assess risk posture. Running FreeIPA does not tell you whether your Linux estate is compliant — it only manages the portion you have explicitly enrolled and maintained. For organisations that have been running Linux estates for years, the drift between what FreeIPA thinks the estate looks like and what it actually looks like is often the real problem.
Deployment reality: FreeIPA is a production service in its own right, requiring high availability configuration, regular maintenance, and genuine expertise to operate correctly. The operational cost is real even if the licence fee is not.
Best suited for: Teams building or standardising their Linux identity infrastructure who want open-source, Linux-native centralised identity management. Not suitable as a standalone compliance or audit tool.
Teleport: Certificate-Based Infrastructure Access
What it is: Teleport is a modern infrastructure access platform built around short-lived certificates and just-in-time access. Rather than managing standing credentials, Teleport issues cryptographic certificates scoped to specific tasks and contexts, which expire automatically. It supports SSH, Kubernetes, databases, and web applications behind a unified access plane.
What it does well on Linux: Teleport's approach to Linux SSH access is genuinely progressive. By replacing long-lived SSH keys with short-lived certificates, it eliminates the SSH key sprawl problem for sessions that go through Teleport. Its audit log provides a complete record of who accessed what server, when, and what commands were run. For cloud-native environments with a developer access use case, Teleport is elegant.
What it does not do: Teleport governs access that flows through its proxy. It does not inventory the Linux identity topology that exists outside its control plane — the local accounts, sudo rules, service account memberships, and authorized_keys entries that were there before Teleport was deployed, or that exist on systems not yet enrolled. It does not produce compliance evidence for NIS2 Article 21 or DORA ICT risk management controls that require evidence of your overall access control posture — not just the sessions recorded through a proxy.
Deployment reality: Teleport is primarily designed for developer-to-infrastructure access patterns in cloud-native environments. It is an excellent tool for its intended use case. Retrofitting it across a large, heterogeneous Linux estate — particularly one with legacy systems, embedded Linux, or OT-adjacent infrastructure — is complex and often impractical.
Best suited for: Cloud-native engineering teams that want zero-standing-privileges access to infrastructure, with a strong developer experience and cryptographic audit trails.
Delinea: Vaulting Plus Unix Privilege Elevation
What it is: Delinea is an enterprise PAM vendor formed from the Thycotic and Centrify merger, and it is one of the platforms teams weigh when they need Linux privileged access under the same roof as their Windows and cloud secrets. Its core is Secret Server for credential vaulting, paired with a Server Suite and Privilege Manager lineage that brings Active Directory bridging and sudo-replacement policy to Unix and Linux hosts.
What it does well on Linux: Delinea's Centrify heritage gives it genuine Unix and Linux depth: it can join Linux servers to Active Directory, broker privileged sessions, record them for playback, and grant just-in-time elevation instead of standing root. For organisations centralising Windows and Linux credentials in one vault with session capture, that breadth is a real strength.
What it does not do: Delinea governs the accounts and policies it onboards. It does not inventory and risk-score the sudoers rules already scattered across your fleet, audit the SSH key lifecycle on each host, surface stale or orphaned accounts, or map the non-human identities — service accounts, pipeline credentials, API keys — that accumulate outside its control. Its compliance output describes managed sessions, not the true state of your Linux identity estate.
Deployment reality: Server Suite and Secret Server are substantial platforms; AD bridging, agent rollout, and policy design take planning and licensing budget, and consolidating two formerly separate product lines — Thycotic vaulting and Centrify Server Suite — can mean navigating overlapping consoles during migration.
Best suited for: Enterprises that want credential vaulting, session recording, and AD-integrated privilege elevation for Linux and Windows under a single console.
StrongDM: Brokered Infrastructure Access
What it is: StrongDM is an infrastructure access platform that sits between users and Linux servers, databases, and Kubernetes clusters, brokering every connection through a central proxy. Teams evaluate it as a Linux PAM alternative when they want to remove standing SSH keys and credentials from hosts and route access through identity-aware, logged sessions instead.
What it does well on Linux: StrongDM authenticates users against your identity provider, injects credentials they never see, and records full session activity to Linux targets for replay and audit. Because access is brokered just in time, it can eliminate the shared, long-lived SSH keys that normally pile up on servers, and it enforces role-based, time-bound access cleanly.
What it does not do: StrongDM governs what flows through its proxy. It does not inventory or risk-score the sudo rules on each host, audit the SSH keys and authorized_keys files that already exist across the estate, detect stale accounts, or map privilege-escalation paths and non-human identities living outside the proxy. Its logs prove what happened in brokered sessions, not whether your underlying Linux identity posture is sound — the evidence auditors increasingly ask for.
Deployment reality: StrongDM introduces a proxy tier and gateway infrastructure to run and secure, and its value depends on onboarding every target and routing all privileged access through that plane with gateways kept highly available.
Best suited for: Engineering teams that want a single, logged access plane brokering developer connections to Linux servers, databases, and Kubernetes, and that are willing to make the proxy the mandatory path for every privileged connection.
HashiCorp Vault and Boundary: Dynamic Secrets and Session Brokering
What it is: HashiCorp Vault and Boundary are two complementary tools teams reach for when they want programmatic, identity-based access to Linux infrastructure. Vault manages secrets and issues dynamic, short-lived credentials; Boundary brokers user sessions to Linux hosts without distributing standing credentials. Together they are a common cloud-native answer to the Linux PAM question.
What it does well on Linux: Vault's SSH secrets engine can issue signed, short-lived certificates or one-time passwords, replacing static SSH keys with credentials that expire. Boundary grants just-in-time, identity-scoped access and, in recent versions, records sessions. For infrastructure-as-code shops, dynamic secrets and ephemeral access fit naturally into automated Linux pipelines.
What it does not do: Neither tool inventories the sudo rules already present on your servers, risk-scores sudoers drift, audits the SSH keys sitting in existing authorized_keys files, flags stale or orphaned accounts, or maps the privilege-escalation paths across your fleet. Vault secures the secrets you route through it, but the non-human identities and access paths outside it — and audit-grade evidence of your overall Linux posture — remain unaddressed. In practice most teams run Vault primarily as a secrets store, so day-to-day Linux access governance still falls to scripts and manual review.
Deployment reality: Vault and Boundary are powerful but operationally demanding: high-availability clusters, secret-engine configuration, and policy management are ongoing engineering commitments, and running both products well is a dedicated platform-engineering responsibility rather than a turnkey PAM deployment.
Best suited for: Platform and DevOps teams standardising on HashiCorp tooling that want dynamic secrets and brokered, short-lived access to Linux infrastructure, and that have the engineering capacity to operate both products in production.
Okta Privileged Access: Zero-Standing-Privilege Server Access
What it is: Okta Privileged Access is Okta's PAM offering — built on the ScaleFT and Advanced Server Access lineage — that extends Okta identities to Linux and Windows servers. Organisations already standardised on Okta consider it when they want privileged Linux access governed by the same identity provider that runs their single sign-on, rather than introducing a separate vault and a separate directory to administer alongside it.
What it does well on Linux: Okta Privileged Access issues ephemeral, certificate-based credentials for SSH so users log in without static keys, ties server access and sudo entitlements to Okta groups and policies, and captures privileged sessions. Zero-standing-privilege access and just-in-time elevation, driven by existing Okta identities and MFA, are its clear strengths, and joiner-mover-leaver changes made in Okta propagate to server access automatically.
What it does not do: Okta Privileged Access controls the access it grants. It does not inventory and risk-score the sudo rules already configured across your hosts, audit the SSH key lifecycle on each server, surface stale accounts, or map privilege-escalation paths and non-human identities that exist outside Okta's control. Its records show governed sessions, not an audit-ready picture of your actual Linux identity estate — the evidence NIS2, DORA, and PCI assessors expect.
Deployment reality: It requires the Okta platform, a server agent on each Linux host, and policy configuration, so value depends on being an Okta-centric organisation.
Best suited for: Okta customers that want zero-standing-privilege, ephemeral-credential access to Linux servers tied to their existing identity fabric, and that already treat Okta as the system of record for every workforce identity.
LinuxGuard: Privilege Topology and Audit Evidence
What it is: LinuxGuard is a Linux-native identity visibility and audit platform. Where other tools manage or control privileged access, LinuxGuard maps the complete privilege topology of your Linux estate — every user, group, sudo rule, SSH key, PAM configuration, and service account — and shows you the paths an attacker would exploit, whether or not those paths exist inside any managed access control system.
What it does well on Linux: LinuxGuard was built exclusively to be the control plane for Linux Identity. Its audit engagement deploys lightweight, read-only collectors that gather identity artefacts across your entire estate, no authentication flow changes, no operational impact. The output is a complete privilege map: who can escalate to root via which sudo rules, which service accounts have overprivileged group memberships, where SSH keys are shared across systems, which authorized_keys entries point to accounts that no longer exist.
The compliance evidence package maps findings directly to NIS2 Article 21, DORA ICT risk management controls, CIS Benchmark, SOC 2 CC6, PCI DSS, NIST 800-53, ISO 27001, SOX, and HIPAA — in a format designed for auditors, not security engineers.
What it does not do: LinuxGuard is not a credential vault. It does not broker sessions, rotate passwords, or replace your authentication infrastructure. It is a next-generation PAM built around visibility and gated response — it maps and governs what every identity, human, service account or agent, can do on the host, and contains a compromised identity behind an approval — rather than a vault or a session broker. If you need to vault privileged credentials or record sessions, you will need a separate tool for that.
Best suited for: Security teams, CISOs, and compliance officers who need to know the actual identity and privilege posture of their Linux estate — either as a standalone audit engagement, as a pre-deployment baseline before introducing PAM tooling, or as ongoing continuous monitoring between annual audits.
Comparison at a Glance
The gaps in the table below are the same ones that surface when you compare a PAM platform against Linux-native tooling directly: what your PAM platform misses.
| Capability | CyberArk | BeyondTrust | FreeIPA | Teleport | Delinea | StrongDM | HashiCorp | Okta PA | LinuxGuard |
|---|---|---|---|---|---|---|---|---|---|
| Linux-native | 🟡 Partial | 🟡 Partial | 🟢 Yes | 🟡 Partial | 🟡 Partial | 🟡 Partial | 🟡 Partial | 🟡 Partial | 🟢 Yes |
| Sudo risk | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🟢 Yes |
| SSH key audit | 🟡 Partial | 🔴 No | 🔴 No | 🟡 Partial | 🔴 No | 🟡 Partial | 🟡 Partial | 🟡 Partial | 🟢 Yes |
| Stale accounts | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🟢 Yes |
| Privesc paths | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🟢 Yes |
| Credential vaulting | 🟢 Yes | 🔴 No | 🔴 No | 🟡 Partial | 🟢 Yes | 🟡 Partial | 🟢 Yes | 🟡 Partial | 🔴 No |
| Session recording | 🟢 Yes | 🔴 No | 🔴 No | 🟡 Partial | 🟢 Yes | 🟢 Yes | 🟡 Partial | 🟢 Yes | 🔴 No |
| JIT access | 🟢 Yes | 🔴 No | 🔴 No | 🟡 Partial | 🟢 Yes | 🟢 Yes | 🟢 Yes | 🟢 Yes | 🔴 No |
| Estate-wide privilege inventory | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🔴 No | 🟢 Yes |
Can You Use CyberArk, Teleport and LinuxGuard Together?
These tools are not always direct alternatives. For many organisations, the answer is a combination — and understanding the sequencing matters.
The most common mistake is deploying CyberArk or BeyondTrust without first mapping what you have. You end up with a vaulted subset of known privileged accounts and session recordings for managed access — while the sudoers files, orphaned accounts, shared SSH keys, and service account privilege creep that existed before the deployment continue to represent your actual exposure. The tool creates an audit artefact. It does not create security.
The right sequencing:
- Map first. Use LinuxGuard to establish what your Linux identity posture actually looks like — before deploying any access control tooling. This gives you a remediation baseline, a compliance evidence package for immediate regulatory needs, and a prioritised picture of where control tooling will have the most impact.
- Remediate the worst findings. Orphaned accounts, NOPASSWD rules, shared SSH keys, and overprivileged service accounts can be cleaned up directly — they do not require a PAM platform, they require someone to action them.
- Deploy access controls where they add value. CyberArk or BeyondTrust for session brokering and credential vaulting on the highest-risk systems. Teleport for developer-to-infrastructure access in cloud-native environments. FreeIPA for building out centralised Linux identity infrastructure on a clean baseline.
- Monitor continuously. Use LinuxGuard's continuous drift detection to surface new privilege drift, unauthorised SSH key additions, and emerging escalation paths between annual audits — so the next audit starts from a clean baseline rather than uncovering twelve months of accumulated exposure.
The Compliance Evidence Gap: What NIS2, DORA and SOC 2 Actually Require
This is the dimension most often missing from PAM evaluations — and the one that matters most to CISOs, audit committees, and regulators in 2026.
Under NIS2 Article 21, covered entities must implement and be able to demonstrate access control policies as part of their cybersecurity risk management measures. Under DORA's ICT risk management framework, financial entities must document and evidence ICT access controls as part of their operational resilience posture. Under SOC 2 CC6, auditors require evidence of logical access controls including least-privilege implementation.
Session recordings show what happened in recorded sessions. Audit logs show commands that ran through managed access paths. Neither answers the question an auditor is actually asking: "Show me your access control posture. Show me who had what access, on which systems, and whether it was appropriately governed."
That question requires an inventory of your Linux identity estate — not a log of sessions that happened to flow through a proxy. LinuxGuard produces that inventory, maps it to the specific control language of each framework, and generates a structured evidence package that goes directly into your audit file. No spreadsheet assembly. No screenshot gathering. No six-week manual exercise before every audit.
When to Choose LinuxGuard — and When to Choose CyberArk, BeyondTrust or Teleport
Three of these comparisons now have their own Linux-qualified pages, each opening with who LinuxGuard is best for: LinuxGuard vs CyberArk for Linux, LinuxGuard vs Teleport for Linux and LinuxGuard vs BeyondTrust for Linux.
You should be talking to LinuxGuard if:
- You are preparing for an NIS2, DORA, SOC 2, PCI DSS, or ISO 27001 audit and need Linux access control evidence in a format regulators accept
- You have never formally audited your Linux identity posture and cannot say with confidence how many orphaned accounts, NOPASSWD sudo rules, or shared SSH keys exist across your estate
- You are evaluating CyberArk, BeyondTrust, or Teleport and want to understand your actual baseline before you deploy
- You have already deployed a PAM platform and a recent audit revealed findings in the Linux identity layer that the platform did not surface
- You are a CISO who can confirm your Windows estate is governed but cannot say the same about every Linux server
- You need to demonstrate continuous compliance to an audit committee or board between annual audits
LinuxGuard is not the right fit if:
- You need credential vaulting or session recording for known privileged accounts — CyberArk or BeyondTrust is the right tool for that
- You need just-in-time, zero-standing-privilege access for developers in a cloud-native environment — Teleport is purpose-built for that use case
- You are building out Linux identity infrastructure from a greenfield state — FreeIPA or Red Hat IdM provides a strong foundation
- You need enterprise credential vaulting with Unix and Linux privilege elevation and session recording under one console — Delinea (Secret Server with its Server Suite heritage) is built for that
- You need a single access proxy that brokers and logs developer sessions to Linux servers, databases, and Kubernetes — StrongDM is designed for that
- You need dynamic secrets and short-lived, identity-based access to Linux infrastructure as code — HashiCorp Vault and Boundary fit that model
- You need zero-standing-privilege, ephemeral-credential access to Linux servers tied to your existing Okta identities — Okta Privileged Access is purpose-built for that
Where a Scripted Audit Stops Holding Up
Most teams start here, and on a handful of servers it works. A shell script or an Ansible playbook can pull the sudoers file and its includes, the authorized_keys files and the local account list from a host, and a careful engineer can read the result. Nothing about that is wrong. It is the right first step.
It stops holding up at estate scale, for reasons that have little to do with the script itself. Coverage drifts: hosts are built, rebuilt and retired between runs, and the inventory the script iterates over is itself one of the things you are trying to audit. The output is a snapshot per host, so the questions that matter across hosts go unanswered: which key appears on dozens of servers, and which account can reach root on which of them, through which chain of group membership, sudo rule and include file. Effective privilege has to be resolved, not listed. Aliases, nested groups, wildcards and NOPASSWD entries only mean something once they are evaluated together. And a snapshot cannot say who changed a rule or when, which is the first thing an auditor asks.
Then there is the script. It needs an owner, a schedule, credentials of its own with read access to every host, and maintenance every time a distribution changes a path or a default. What it produces is a directory of text files that someone has to turn into evidence an assessor accepts, again, for each framework. None of this makes scripting a mistake. It makes it a starting point. Once the estate is too large for anyone to hold the output in their head, the job has become continuous inventory, resolution and attribution, which is what LinuxGuard was built for. The side-by-side with manual effort is on Why LinuxGuard.
Why Visibility Comes Before Control
The tools that attract the biggest budgets in privileged access management are control tools. They are good at what they do. But you cannot control what you cannot see.
79% of modern enterprise attacks use no malware. They exploit credentials and access paths that were already there, already misconfigured, already forgotten. No session recording surfaces a NOPASSWD sudo rule sitting in a sudoers file since 2021. No credential vault catches a service account with membership in a privileged group that nobody remembered to review.
The first question is not which tool controls your Linux access. The first question is: do you know what your Linux identity posture actually looks like?
If you cannot answer that with confidence, that is where to start.
Frequently asked questions
What is a PAM tool?
A PAM (Privileged Access Management) tool secures, controls and monitors accounts with elevated rights — vaulting credentials, brokering sessions and logging privileged activity. Most were built for Windows and network devices. On Linux, privilege lives in sudo rules, SSH keys, group memberships and service accounts that traditional PAM never maps.
What is the best PAM tool?
There is no single best PAM tool — it depends on your estate. CyberArk and BeyondTrust lead for credential vaulting and endpoint privilege control, Teleport for certificate-based infrastructure access, and FreeIPA for centralised Linux identity. For Linux privilege visibility and audit evidence — who can actually reach root, and proof auditors accept for NIS2, DORA and SOC 2 — LinuxGuard closes the gap those tools leave.
Is PAM difficult to implement?
Traditional PAM can be: credential vaults, session proxies and agent rollouts often take months and change how administrators work day to day. Mapping Linux privilege is lighter. LinuxGuard uses a lightweight agent, packaged for Debian, RPM and Alpine hosts, whose collection is read-only. It makes no changes to authentication, the only thing that alters a host is a response action someone has approved, and it delivers a complete privilege map in days rather than a quarter-long rollout.
What are common PAM mistakes?
The most common mistakes: vaulting credentials while leaving sudo rules, SSH keys and service accounts ungoverned; treating authentication as the finish line instead of mapping what an identity can actually do once inside; and collecting logs without turning them into audit-ready evidence. On Linux, privilege drift accumulates in exactly the places traditional PAM does not watch.
Get the Full Picture in Days
The LinuxGuard Pilot maps every user, group, sudo rule, SSH key, PAM configuration, and service account across your Linux estate. Fixed scope. Fully remote. Board-ready compliance evidence included.
Schedule a 30-minute scoping call →
Peter Cummings is the founder of LinuxGuard and has 20+ years of IAM and security architecture experience at Mastercard, EY, UBS, Lonza, and UK Government agencies.